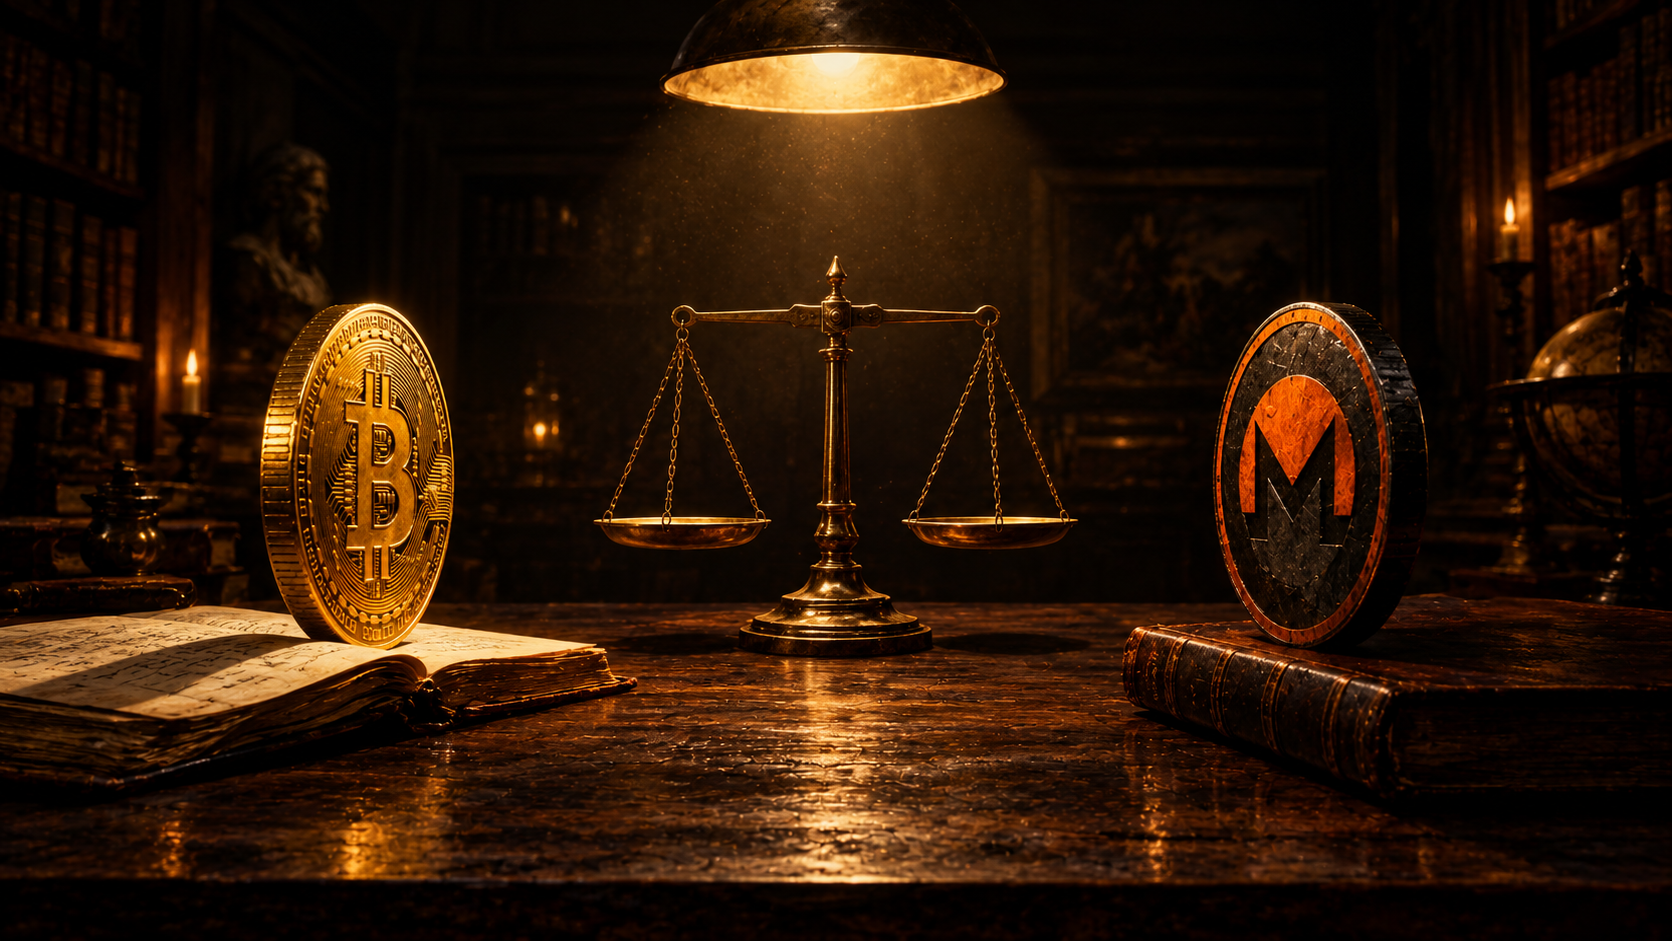
Bitcoin vs. Monero: Six Arguments Neither Side Can Win
I set Bitcoin and Monero against each other in six arguments. Neither one won all of them.
The Question#
Bitcoin and Monero are usually discussed as rival teams, which flatters the fans and teaches very little. The more useful question is what each system chose to give up. Every monetary design is a bundle of trade offs, and underneath the noise, the quarrel between these two camps is a quarrel about which costs a person should be willing to carry.
So I built six disputes, each around a trade off neither side can fully escape. Each side makes its strongest case and has to answer the other's. Every factual claim was checked against the record as of October 2026, and that includes the facts that embarrass the side making the argument.
I. Scarcity Against Fungibility#
Money has to satisfy two demands that pull against each other. It must be scarce enough to carry effort forward through time, and uniform enough that any unit can stand in for any other. Bitcoin optimized for the first. Monero optimized for the second.
Bitcoin. Scarcity is the one property that cannot be retrofitted. My supply ends at 21 million, and that limit is enforced by every node that checks a block. A saver is making a bet across decades, so what he needs most is a schedule that no future majority will reopen when it becomes convenient. Weak fungibility can be patched with better tools. A broken cap stays broken, because trust in a monetary limit does not regrow once it has been spent.
Monero. Fungibility is the precondition for money, and on your chain it already fails in practice. Regulated exchanges score coins by their history and freeze deposits that cross a risk threshold. After the 2025 Bybit hack, funds that touched the stolen coins were flagged and frozen across regulated exchanges, and at least one swap service said it would refuse coinjoins that included the blacklisted addresses. A coin whose acceptability depends on its biography is only partly money. As for my supply, it follows a published schedule. Since mid 2022 miners receive a flat 0.6 XMR per block, which works out to well under one percent a year and falls every year. A prominent Bitcoin developer argued in 2022 that with coins steadily lost, a fixed reward converges on a stable supply.
Bitcoin. A small, permanent, declining drip is still permanent dilution, and holders feel it as a tax on patience. The taint problem lives in the compliance layer, outside the protocol. My rules treat every satoshi identically. Fix the surveillance and the uniformity returns. Monero would have to change its rules to cap its supply.
Monero. And your security budget depends on a fee market that has never been tested without a subsidy. Your block reward halves toward zero, so at some point fees alone must pay for the most expensive defense in the history of money.
This dispute does not resolve, because it is really a disagreement about time horizon. A person thinking in decades weights the cap. A person spending this week weights uniformity. Bitcoin's taint problem is real, though it sits in the institutions around the protocol. Monero's emission is predictable, though it is not finite. Each side is describing the cost of the other's choice accurately.
II. The Auditor's Dilemma#
Transparency is what lets anyone audit a ledger, and it is also what lets anyone watch the people using it. Concealment protects the users, and it also hides mistakes. A monetary system has to decide which of those failures it would rather live with.
Bitcoin. On my chain the audit is arithmetic. Any node can total every output and confirm that no coin exists that should not. That matters most when something goes wrong. In September 2018 a bug was found in Bitcoin Core that would have let a miner spend the same coins twice and inflate the supply. It was disclosed responsibly, patched within days, and never exploited on the main network. Had anyone used it, the extra coins would have been visible to the entire world.
Monero. The coins I mint are public, and anyone can check that issuance follows the schedule. What I hide is amounts in transit, and the proofs attached to every transaction guarantee that hidden amounts cannot create money from nothing. My researchers proved the model works under pressure. In February 2017 they found a flaw in the CryptoNote design I inherited that allowed unlimited coins to be minted. They scanned the chain, confirmed it had never been used, and patched it quietly before warning the other projects built on the same code.
Bitcoin. Your own disclosure said the bug was undetectable to an observer unless they knew about the flaw and went looking for it. That is the point. Bytecoin, the coin your code came from, was exploited, and roughly 693 million coins were created through it. Your users are trusting that every unknown flaw will also be found by honest researchers first.
Both chains have survived an inflation bug, and both handled it well. The asymmetry is about unknown unknowns. A transparent ledger exposes a failure even when nobody understood the bug in advance. A private ledger relies on its cryptography being correct, because a quiet failure leaves nothing for an outsider to see. Bitcoin's audit is cheaper and more robust to surprise. Monero's record is clean, and keeping it clean depends on a smaller number of people doing very hard math correctly.
III. Industrial Security Against Open Mining#
Proof of work turns security into a cost. The question is who can afford to pay it, and who could afford to turn it against the network.
Monero. I will go first, because this is where I am weakest and I would rather say so plainly. In 2019 I moved to an algorithm called RandomX so that ordinary processors could mine competitively. I did it on purpose, to keep specialized hardware makers and the few firms that control them from becoming gatekeepers. Mining my chain is something a person can still do at home. The price of that openness is that general-purpose computing power can be pointed at me from elsewhere.
Bitcoin. Which is exactly what happened in 2025. A project called Qubic paid miners more than your own pools did, redirected their machines at your chain, and announced it had seized majority control. There was a six-block reorganization, and several exchanges paused withdrawals. My hashrate is anchored in specialized machines and a vast amount of electricity. To attack me, someone would have to build or buy an enormous fleet of hardware that is useless for anything else, and that cost is the defense.
Monero. The researchers who later went block by block found that Qubic never held a lasting majority and never earned more than honest mining would have paid it. What it did cause was a burst of orphaned blocks and some deeper reorganizations. Most services wait ten confirmations before crediting a deposit, so the six block event did not reach credited payments. Your defense has a concentration problem of its own. As of mid-2026, four pools produced more than 70 percent of your blocks, and one of the two largest is closely tied to Bitmain, the dominant maker of the machines themselves.
Bitcoin wins this dispute decisively. Security is measured in what an attack costs, and commodity hardware lowers that cost for the honest and the dishonest alike. Monero's choice makes it more democratic to secure and cheaper to disrupt, and at its current size the second effect matters more. Bitcoin's concentration in manufacturing and pools is a real political risk. It has not yet translated into a demonstrated attack the way Monero's openness did.
IV. Privacy as a Public Good#
Privacy on a ledger behaves less like a personal preference and more like a public good. Your cover depends on how many other people look exactly like you. When privacy is optional, the few who choose it form a small, conspicuous group, and the choice itself becomes a signal. That is the structural argument for Monero, and it deserves to be tested against the evidence on both sides.
Monero. Every transaction on my chain hides who paid whom and how much, so the crowd you hide in is everyone. The Samourai case shows what happens otherwise. Two developers built a Bitcoin wallet that never held anyone's coins, and in November 2025 they were sentenced to five and four years in prison. On a transparent chain, reaching for privacy marks you before you have done anything at all.
Bitcoin. Those two pleaded guilty, and prosecutors showed that one of them pitched the service on a darknet forum as a way to clean dirty coins. Their conduct was on trial along with their code. Meanwhile the tools keep maturing. Lightning payments are onion routed, so each node sees only the hop before it and the hop after. Silent Payments give a person one reusable address with no public link between the payments it receives, and Sparrow shipped full receiving support in May 2026. Cashu ecash uses blind signatures, so the mint cannot connect what it issues to what gets spent, and nutzaps already carry it across Nostr.
Monero. Each of those requires a choice, and each one carries a trust point. Ecash is only as reliable as the mint you pick. Silent Payments on a phone usually means letting someone else's server scan the chain for you, and Bitcoin Core had no released wallet support for it as of mid 2026. Lightning channels still open and close in public.
Bitcoin. Then account for your own leaks. A 2018 study from Princeton and Carnegie Mellon researchers found that in your early years, about 62 percent of transaction inputs that used decoys could be traced by elimination, and the real input was usually the newest one in the ring. That history is permanent. In 2024 a leaked Chainalysis training video showed the firm tracing Monero users through nodes it operated, logging the IP addresses of wallets that connected to them. Your privacy also costs real resources. A full Monero node held about 250 GiB as of January 2026, and every transaction is several times larger than a typical Bitcoin one.
Monero. Those weaknesses were found, published, and answered. The flaws in that study came from an era when decoys were optional, and mandatory minimums and better decoy selection followed. The Chainalysis method works on people who connect to a stranger's node, and it fails against anyone running their own. The upgrade now in testing, FCMP++, replaces the ring of 16 with the entire set of outputs on the chain, more than 150 million of them. Its latest test network forked on October 5, 2026.
Monero wins this dispute on structure. Because privacy is collective, a system where everyone is covered provides more protection than a system where the careful few are covered and visible. But default privacy is a long way from perfect privacy. Both chains leak at the edges. Network metadata and history recorded before the defenses improved are real exposures, but the worst leak on either chain is the on ramp, where a name meets a coin. Bitcoin's privacy tools are real and getting better. They remain choices, and choices are what get noticed.
V. Who May Change the Rules?#
A monetary system makes a promise about the future, so how its rules change matters as much as what the rules say today. Bitcoin treats change as a threat to be resisted. Monero treats change as maintenance.
Bitcoin. My rules are hard to change on purpose. When altering consensus requires near unanimous agreement among people who distrust each other, the rules a saver relies on today will very likely be the rules his grandchildren inherit. That friction is the product. A system that upgrades on schedule is a system whose holders are always trusting the next schedule.
Monero. I upgrade by scheduled hard fork, and the main chain has carried on through every one of them. I changed my mining algorithm in 2018 and again in 2019 to keep specialized hardware out, and the privacy I offer today is far stronger than what I launched with. Cryptography improves and adversaries adapt. A privacy system that cannot change is one that slowly stops being private.
Bitcoin. And every one of those changes required trusting that your developers chose well.
Monero. Your rules are not as settled as you suggest. Your node operators split over relay policy, and Bitcoin Knots, the stricter alternative, grew to roughly a quarter of public nodes by early 2026. More seriously, a draft proposal called BIP-361 would phase out quantum-vulnerable addresses over five years and freeze any coins that never migrate. That is somewhere around 6.7 to 6.9 million bitcoin, including about 1.7 million attributed to Satoshi. A protocol that sells itself on property rights is openly debating whether to freeze coins that belong to people who never moved them.
Bitcoin. It is a draft, and it is fiercely contested. The difficulty of passing anything like it is the protection you are describing as a weakness. The quantum-resistant address type that did get merged, BIP-360, is optional and forces nobody.
This is the most underrated dispute of the six, because both positions carry a tail risk. Bitcoin's danger is being unable to change on the day it must, and the quantum debate is the first serious test of that. Monero's danger is changing because it can, which concentrates trust in a small group of researchers and developers. Ossification protects a saver from his own community. Adaptation protects a user from his adversaries. Neither protection is free.
VI. Legitimacy Against Sovereignty#
States do not need to ban a currency to shape it. They only need to decide which doors stay open. Bitcoin walked through the doors. Monero was shown out of them.
Bitcoin. Acceptance is a form of protection. Spot Bitcoin ETFs took in $2.39 billion in the week ending September 25, 2026, the strongest week of the year, and public companies keep adding me to their balance sheets. Once an asset sits in ordinary brokerage accounts, outlawing it becomes politically expensive. Deep markets also matter to an ordinary holder, because the day he needs to sell, someone will be there to buy.
Monero. A share of an ETF is a claim on a coin someone else holds, under rules someone else writes. That is legitimacy purchased with custody. I took the other road. More than 70 exchanges delisted me through 2025, and from July 2027 a European anti money laundering regulation bars regulated firms there from handling privacy coins at all. Owning me remains legal in the United States and most major economies. I reached my all-time high of $797.73 in January 2026 anyway, and people now trade me directly through peer to peer markets like Haveno and through atomic swaps with Bitcoin.
Bitcoin. A market that lives outside the doors is thinner and harder to exit in a hurry. Liquidity is a kind of safety you only notice once it is gone.
Monero. And every regulated account you open records your name beside your coins permanently. Your front door keeps a guest book.
This one splits evenly, because each side bought something real and paid for it. Bitcoin purchased liquidity and political cover, and the price was a paper trail that follows most of its users. Monero purchased independence from the gatekeepers, and the price was a narrower market and the constant possibility of being squeezed further. Which bargain looks better depends on whether you expect the institutions around you to stay friendly.
The Verdict#
Tallied up, Bitcoin took security and the audit. Monero took privacy. The remaining disputes came out as genuine trade offs, with each side describing the other's cost accurately. That pattern says something more interesting than a score would. These are two answers to two different threats, built by people who agree on the enemy and disagree about where it will strike first.
Bitcoin is a defense against debasement. Its design assumes the greatest danger to ordinary people is a money supply that can be expanded by whoever controls it, so it buys verifiable scarcity and pays for it in transparency. Monero is a defense against surveillance. Its design assumes the greatest danger is a ledger that lets anyone with resources map a person's life, so it buys concealment and pays for it with a harder audit and a thinner security margin.
There may be no way to have both properties at full strength in one system, because a ledger that anyone can audit completely is a ledger that anyone can read. If that tension is real, a person who wants both protections will hold two instruments. Families have always done this with a savings account and the cash in a wallet. The bridge already exists, too. Atomic swaps let the two be exchanged directly, without asking a third party for permission.
I started this exercise expecting to pick a side, and what I found was a better question. The useful thing to ask is which threat you are guarding against today, and whether you have been honest with yourself about the other one. I had spent years treating debasement as the real danger and surveillance as paranoia. Running the argument fairly cured me of that, and I suspect it would do the same for most people willing to give the other side its best case.
LIGHTNING ADDY: Contra@rizful.com
XMR ADDY: 83odEn5ipbXMX4cz6iQbBNMfpgzYRoJ4BZ8KZHmvQ2cZdd8UHGkgUgfYxHm83eqtMsBPRkEs16LADidutF7AkZBcJaAZkq1
Sources#
- Spark: Tail emission glossary
- Peter Todd on tail emission, bitcoin-dev list
- Monero network stats 2026
- Spark: Taint analysis and fungibility
- Stacker News: Boltz on Bybit hack funds frozen at exchanges
- Bitcoin Optech: CVE-2018-17144
- Bitcoin Core: CVE-2018-17144 full disclosure
- Monero: Disclosure of a major bug in CryptoNote currencies
- Report on Bytecoin coins created by the bug
- Monero technical specs: PoW history, node size, Dandelion++
- CoinDesk: Qubic and Monero's hashrate
- The Defiant: Monero reorg and exchange pauses
- ForkLog: Researchers on the alleged 51% attack
- Inside Qubic's Selfish Mining Campaign on Monero (AFT 2026)
- Bitcoin.com News: Four pools control 70%+ of hashrate
- Hashrate Index: Top mining pools of 2026
- Decrypt: Samourai developer sentenced to five years
- Decrypt via Cryptonews: Samourai co-founder sentenced to four years
- Lightning Labs: L402 and onion-routed payments
- Bitcoin Wiki: Silent Payments wallet status
- YakiHonne: Cashu ecash and nutzaps
- Möser et al., An Empirical Analysis of Traceability in the Monero Blockchain (PoPETs 2018)
- Monero's response to the traceability paper
- Cointelegraph: Leaked Chainalysis video on Monero
- Decrypt: Monero expert on the Chainalysis video
- Monero myths: transaction size comparison
- Bitrue: FCMP++ stressnet and mainnet timing
- BlockEden: Core v30 and the rise of Knots
- CoinDesk: Quantum debate and BIP-361
- Deutsche Digital Assets: Quantum clock
- Rankia: Bitcoin ETF inflows, September 2026
- Xgram: Is Monero legal in 2026
- Pluang: Monero all-time high
- Xgram: BTC-XMR atomic swaps and Haveno
Contra
The unexamined premise is the only tyranny that asks for your consent. Prolific thinker. Reformed Christian, Nostr class of 23. 🎶 https://wavlake.com/contra XMR: 85uvRUyfDy4Bc4osouAGmGc1Tw4bFBfPcGZN8wmtfwEjjeDz5JXFza6XrtbgE7WePSM8nuo95eZRYFs2yA9ooUxs2f8sdBB
reformedsaint@zaps.lol The unexamined premise is the only tyranny that asks for your consent. Prolific thinker. Reformed Christian, Nostr class of 23. 🎶 https://wavlake.com/contra XMR: 85uvRUyfDy4Bc4osouAGmGc1Tw4bFBfPcGZN8wmtfwEjjeDz5JXFza6XrtbgE7WePSM8nuo95eZRYFs2yA9ooUxs2f8sdBB